When an AI agent calls a tool on someone's behalf, the question that matters most to a security team is simple: who did this, and were they allowed to? A demo expense-approval agent, built by an engineer at Keycard and a solutions architect at Temporal, shows why a single shared API key cannot answer that question, and how two standards-based pieces of infrastructure can. Keycard applies the OAuth 2.0 Token Exchange standard (RFC 8693) to mint a narrow, short-lived token for every tool call and to record a delegation chain from human to agent to backend. Temporal adds durable execution, so the same agent can survive a process crash without redoing expensive work or losing its ledger state.
Why one shared key is a problem
In many existing agent setups, developers hand the agent a long-lived static API key and let it reach whatever backend it needs. The demo starts from exactly that baseline. An application called Expense Desk lets a person type requests in natural language, such as filing or approving an expense, and a LangChain-based agent turns those requests into tool calls. The agent talks to an Expense MCP server through the Model Context Protocol (MCP), a standard interface for connecting agents to tools, and the MCP server writes to a downstream Ledger API that holds the expense records. Payouts are simulated; nobody gets real money.
In the baseline configuration, every agent connecting to that MCP server uses the same key. Filing a $75 snack expense creates a pending entry whose audit trail says only that access was granted by an API key. Approving another person's $100 expense produces the same result: the status flips to approved, and the log credits the key, not a reviewer. Anyone holding the key can take any action and claim any identity, so the audit trail cannot establish accountability.
Three failures stack up here:
- No attribution: the log cannot distinguish one human or one agent process from another.
- No least privilege: a static key usually grants broad access across a whole service rather than the single action an agent needs right now.
- Weak compensation: a human reviewing agent actions does not close the gap, because reviewers make mistakes and many agents now run without a person watching each step.
How token exchange changes the flow
RFC 8693, an OAuth 2.0 extension published in 2020, lets one party trade a token it holds for a different token scoped to a specific downstream target. Keycard uses it as the core of an identity layer for agents at runtime.
The flow in the demo works like this:
- The human signs in through a standard authorization server (the kind offered by Okta, Auth0 or Google) and consents to delegate a subset of permissions, called scopes. The server issues an identity token for that user.
- That identity token becomes the subject token: proof of the person on whose behalf the agent may act.
- The agent runtime acts as an OAuth client. It authenticates itself to Keycard's Security Token Service (STS) with its own client credentials or workload identity, presents the subject token, and asks for a token good for exactly one tool call on the Expense MCP server.
- Keycard STS checks the request against administrator-defined policy covering which agents, which users, which resources and which operations are allowed. If the call matches, it mints a least-privilege access token for that tool. These tokens expire within minutes and should never be written to long-term storage.
- The agent sends the ephemeral token with the tool request to the MCP server.
- To write to the database, the MCP server performs a second hop: it exchanges the token it received for an even narrower one scoped only to the Ledger API.
- After checking that token, the Ledger API carries out the write and hands the result back. The MCP server then throws the token away as soon as the call completes.
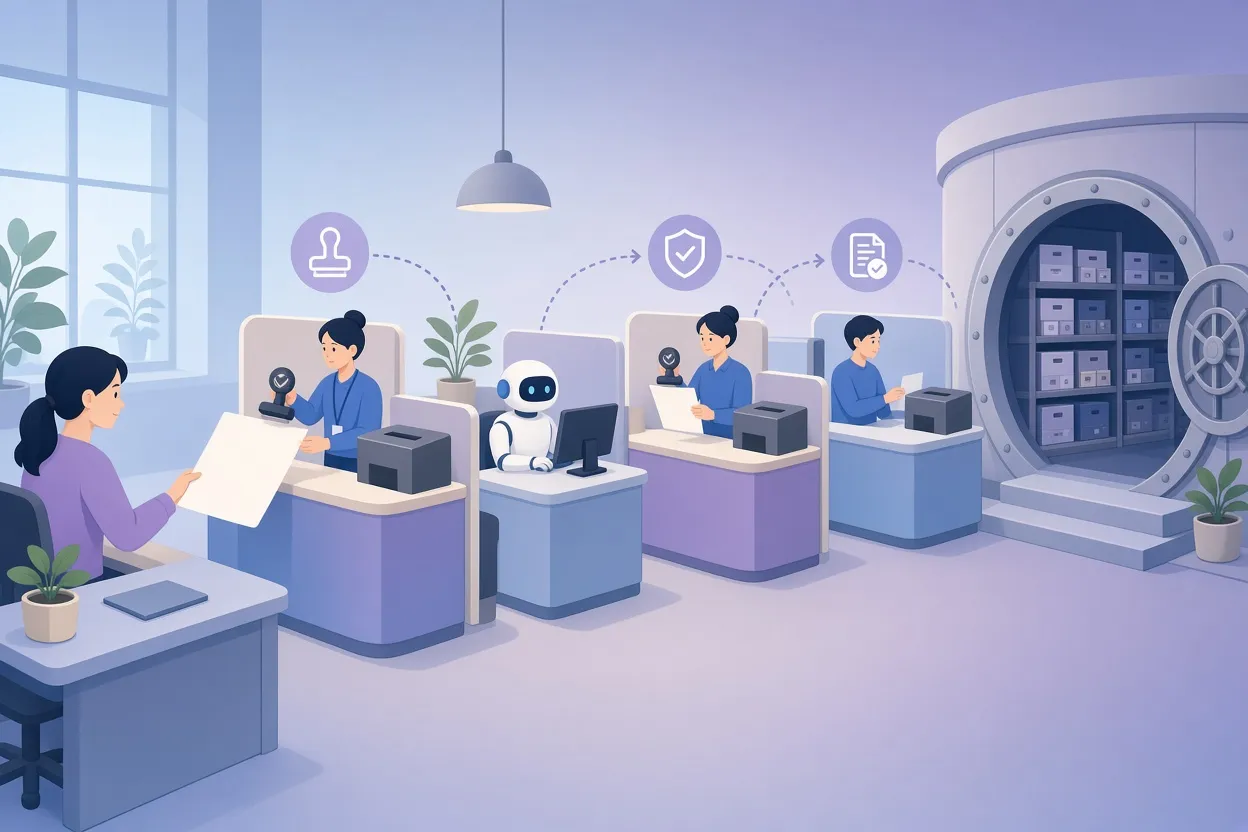
▲ Multi-hop token exchange from user to ledger
At each hop, Keycard captures three things: the agent's identity, the delegating user's identity, and the permission level that was delegated. The OAuth client that drives this can live inside custom agent code, run as an MCP gateway, or wrap an off-the-shelf coding agent as a CLI tool.
Step one: give the agent its own identity
Keycard models two kinds of registrations. An Application is client software that requests tokens or starts exchanges. A Resource is something that protects access and receives tokens. An agent is often both: it requests tokens to call tools, and it receives the user's sign-in token when a person logs in.
Setting this up for the Expense Desk agent took the following steps:
| Step | What was configured |
|---|---|
| Register the application | Name and a unique identifier in URN form, consent mode set to Implicit, and the exact callback URL pulled from the sandbox terminal |
| Register the agent as a resource | A matching URN, Keycard's Zone Provider as credential provider, and the application selected under "Provided by Application" |
| Add dependencies | Four resources: the agent's own resource, the shared Expense MCP resource, an LLM API secret held in Keycard's Vault, and the OpenID Connect UserInfo endpoint |
| Create credentials | A Client ID and Client Secret, shown once, pasted into the agent's environment file |
Two details matter. Omitting the "Provided by Application" link causes exchange requests to fail, because Keycard has no record that the application is allowed to trade user tokens for access to that resource. And the Vault dependency means the LLM provider's key never has to sit in plaintext on the host's disk. Pasting secrets into a local file is acceptable in a throwaway sandbox, but in production the recommended path is workload identity federation or fetching credentials dynamically through the Keycard CLI.
With the code updated so that every tool call requests a scoped token rather than reusing a permanent credential, the agent can run without any user signed in. In that case the subject token is null, and the client SDK falls back to an OAuth client credentials grant: the agent authenticates purely as itself. Asked which account it is using, the agent reported its own identity, Expense Desk Agent, with an approval limit of $49.99. When told to file a $75 expense on behalf of a named employee, it created item EP718 as pending, and the audit record named the agent as the actor. The memo text mentioned a person, but a name typed into a prompt is not verified delegation, so the ledger did not treat it as one.
The Keycard console confirms the chain. Filtering activity by the agent application shows a client_credentials grant targeting the Expense MCP resource, and filtering the shared Expense MCP Actor application by Ledger API calls shows the MCP server acting on behalf of the agent application for the downstream call.
Step two: let the agent act for a user without becoming the user
Application identity alone records which software made a call. It does not say whether a human authorized it. The next stage binds the human in through a real sign-in rather than a claim in the prompt, which required opening Expense Desk in a separate browser tab because embedded frames generally cannot handle external identity-provider redirects.
Once signed in, the user's identity metadata carried a $100 approval limit, while the agent kept its own $49.99 ceiling for autonomous approvals. The resulting behavior shows what fine-grained policy looks like when identity is reliable at every layer:
| Request | Outcome | Reason recorded |
|---|---|---|
| Submit $30 for office supplies | Created on behalf of the user, approved automatically by the agent | Eligible office supplies under $50 with a clear business purpose |
| Submit $75 for printer paper and toner (EXP-123) | Pending, awaiting human review | Exceeds the agent's autonomous limit |
| Approve EXP-123 as the submitter | Refused | "You cannot approve or reject your own expenses. Ask another reviewer." |
| Reject another user's $100 laptop expense (EXP-121) | Rejected, logged under the signed-in user | Human reviewer acting within their authority |
The self-approval refusal is only possible because the system can tell the creator of an expense apart from the would-be approver. Earlier expenses filed under the shared key stayed attributed to the key; adding delegation does not rewrite history.
In the console, filtering by the user's identity reveals the first hop: the agent application exchanged the user's sign-in token for a scoped token targeting the Expense MCP resource, with the subject token, requested resource and granted permissions all recorded. The Expense MCP Actor's log shows the second hop to the Ledger API. Both hops share a session ID, so a security team can follow one request end to end across tiers without losing the human behind it.
Durable execution: what happens when the process dies
An agent loop that calls a model, calls tools, and repeats is a distributed system, and it inherits every distributed-system failure mode: dropped connections, provider outages, killed containers. Without durability, a crash twelve steps into a multi-step task leaves two bad options: rerun everything, paying again for every LLM call, or leave the work half-finished.
Temporal is an open-source durable execution framework that tracks workflow code as it runs and records each state transition. If a worker process dies, Temporal reconstructs the state up to the failure point and resumes from there. Code is split into workflows, which coordinate the high-level steps, and activities, which perform side effects such as ledger writes and external calls. Developers write ordinary Python rather than custom orchestration scripts.
▲ Durable workflow resuming after a crash
The demo settlement workflow includes retry policies, distinct ledger-mutation activities, and a timer modeling a wait for human sign-off. A worker started polling its task queue, a client launched the workflow, and the logs showed the worker debiting and minting an expense token of 4,200 units before pausing at the timer. The worker was then killed with a keyboard interrupt. On restart, Temporal picked the workflow up at the exact point of interruption and ran it to completion: no duplicated ledger entry, no repeated model call. If an outage lasts only seconds, the end user may never see an error.
Keeping tokens out of the event history
Event-sourced engines raise a fair concern: if every workflow input and output is persisted, do short-lived tokens end up in the history? Temporal offers two mechanisms, and Keycard uses the first:
- Activity interceptors are hooks that run around activity execution. A grant_resource decorator on an activity uses an interceptor to fetch the scoped credential just in time, right before the activity runs, so the token never sits in worker memory or workflow state. This holds across fleets of workers or Kubernetes pods.
- Payload codecs run on the client side, in the client process or a sidecar, and encrypt workflow data before it leaves your boundary. Temporal servers and Temporal Cloud then handle only ciphertext and never hold the keys.
A verification script that dumped the full event history for the demo workflow found no JWT material or raw Keycard tokens. Temporal also ships connectors and patterns for OpenAI, PydanticAI and LangChain, and an agentic harness aimed at simplifying resilient multi-step deployments is in development.
What to take from this
The two halves of the design address different risks, and they compose. Identity-aware token exchange makes each agent action attributable, minimal and verifiable; durable execution makes each multi-step task survivable and keeps secrets out of persistent logs.
For teams building agents that touch real systems, the practical checklist that emerges looks like this:
- Retire shared static keys for agents. Give each agent its own cryptographic identity and let it fall back to client credentials only when no human is involved.
- Treat prompt text that says "on behalf of" as unverified. Bind the user through a real sign-in and carry the subject token through every exchange.
- Use multi-hop token exchange wherever an MCP server or other intermediary sits in the path, so each layer holds only the narrow token it needs and discards it after use.
- Write approval limits and separation-of-duties rules against identity metadata, then check audit logs after any change to confirm actors and scopes match expectations.
- Run agent loops on a durable execution engine rather than hand-built database checkpoints and replay scripts, and verify in testing that no tokens or personal data land in event history.
Whether every organization needs this full stack is a judgment call, but the demo makes the trade-off concrete: a shared key is simpler to set up and impossible to audit, while a few registrations and a token exchange turn each agent action into a record of who acted, for whom, and with what authority.


