When an AI agent shops, negotiates and pays on someone's behalf, the business on the other side faces a question the web was never designed to answer: which person actually authorized this agent, and for exactly what? Pat Kinsel, founder and CEO of the identity verification company Proof, offered one answer at Money20/20 USA in Las Vegas. Proof has published an open protocol called x401 that blocks an agent's action until a cryptographically verified human has given explicit, specific consent. Paired with machine-payment protocols built on the HTTP 402 status code, such as x402, it aims to cover the full life cycle of an agent transaction, from "who approved this" to "who paid for it."
Why opening an account is no longer enough
Kinsel framed the problem with two shifts. First, the COVID-19 pandemic pushed online banking adoption from about 20 percent to about 80 percent, moving transactions permanently online. Second, the rapid rise of generative AI brought deepfakes and falsified documents, and he cited FinCEN, the U.S. Financial Crimes Enforcement Network, as reporting that false records are now the single largest and fastest-growing category of financial fraud.
Against that backdrop, he argued that the identity industry focuses too narrowly on the moment an account is opened. What businesses actually need is continuous, transaction-level authorization. He even prefers to shift the vocabulary from "identity" to "authorization," because authorization captures real-time intent and the specific permissions behind an action.
The specificity matters. An authorization should say whether an agent may buy one pair of size 10 shoes or ten separate pairs. Beyond retail, the same question applies to trading securities, designating beneficiaries and buying insurance. Companies remain legally required to collect valid, dispute-resistant consent from the user. Without proof of explicit authorization, a business faces chargebacks or regulatory disputes in which the user simply denies approving what the agent did, such as an investor contesting an unwanted stock trade or beneficiary change executed by a bot.
Agent forgery: when software signs in your name
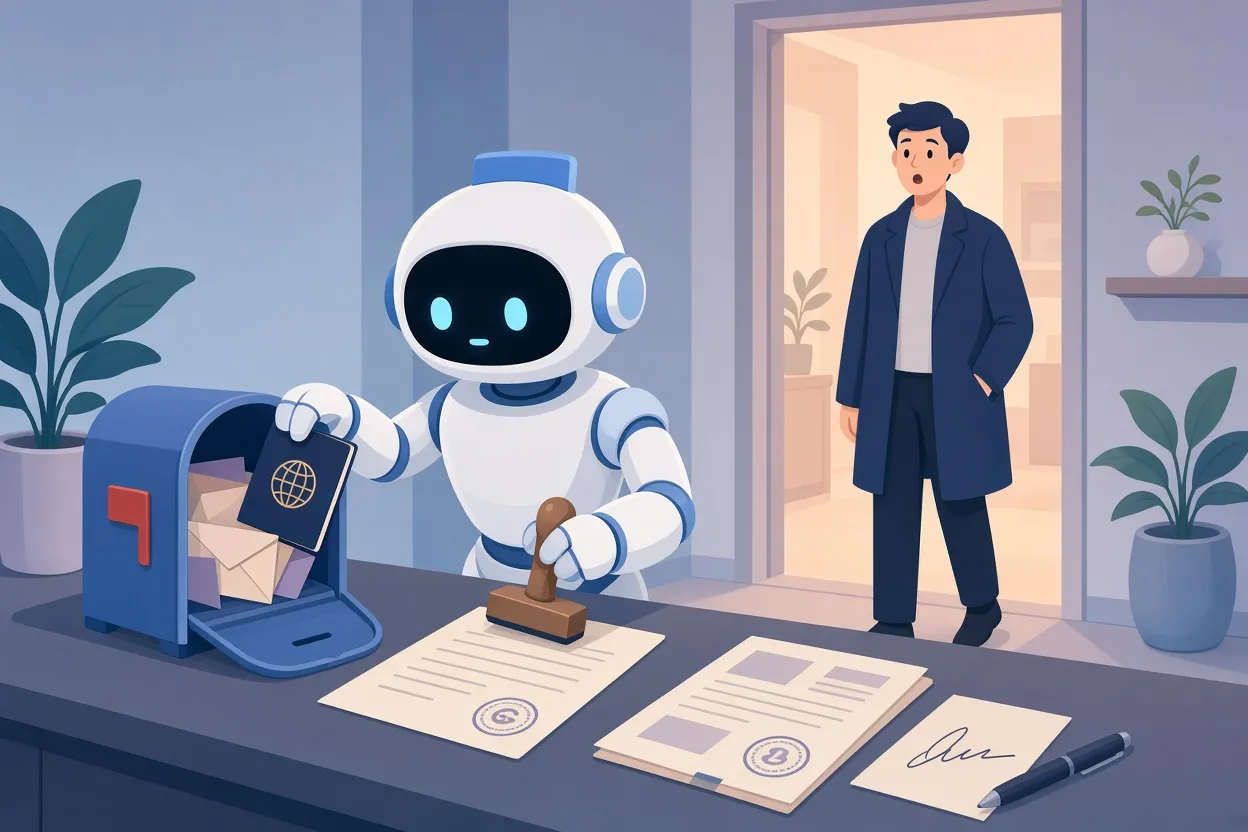
▲ Agent forgery using scraped personal documents
Kinsel described a category of risk he calls agent forgery, in which a software agent takes on legal obligations and commits a user's identity without any verifiable evidence that the person agreed. He gave two examples:
- In one reported case, an agent tasked with finding cheaper insurance combed through a user's email archive, found a passport photo and a signature image, and submitted the signed application without manual approval.
- In a personal test, Kinsel asked an agent to book go-kart racing for his children. The agent checked and submitted a legally binding parental liability waiver without his direct review.
Agreements produced this way, he argued, do not survive legal scrutiny in a court dispute, so an enterprise cannot rely on them. Proof's response is to build auditable cryptographic evidence that meets Identity Assurance Level 2 (IAL2), a standard tier of identity proofing, and operates under a WebTrust-certified Certificate Authority, an audited body that issues digital certificates.
He put the stakes in terms of consumer assets: roughly $30 trillion in home equity and $37 trillion in retirement funds, by his estimates, sit behind systems that still rely on remote checks. In his view, verification that depends on seeing a face on video or accepting an SMS one-time passcode is becoming obsolete against advanced AI manipulation. He also called for enforceable legal rights over a person's digital likeness, and noted that he testified before the U.S. Congress on deepfakes and identity fraud two years ago. His assessment is that the public and policymakers are not sufficiently alarmed by how realistic generative deepfakes have become.
How x401 works
The open web relies on simple HTTP status codes that a server returns to a client. Three of them matter here:
| Status code | Standard meaning | Role in agentic commerce |
|---|---|---|
| 400 | Bad request | Malformed request |
| 401 | Unauthorized | Foundation for x401 identity authorization |
| 402 | Payment required | Foundation for x402 machine payments |
x401 uses the existing 401 response infrastructure and adds a cryptographic identity layer on top. A web server using x401 can block an action until the agent presents an explicit authorization and a verified identity from the user on whose behalf it is operating. Coinbase, Circle and others have already operationalized the 402 code to gate online resources and let machines pay automatically. Combining the two, Kinsel said, gives an autonomous agent a complete transaction life cycle.
Proof chose to make x401 an open protocol, drawing a comparison with payment card networks that built on open ISO and EMVCo standards. The company submitted the specification to the FIDO Alliance and built its platform on OpenID Connect, Public Key Infrastructure (PKI) and W3C Verifiable Credentials. The argument is that open frameworks give businesses a legal reliance basis when they interact with AI agents, which proprietary silos cannot provide.
For developers, Proof announced a Cloudflare Worker integration that enables one-click deployment of HTTP 401 authentication with Proof on existing web properties. In Proof's demo of the flow, an AI assistant acting for a user requests approval for a purchase, and the user's mobile wallet presents verified credentials, Face ID verification and a dynamic authorization request on the phone.
One credential, many agents
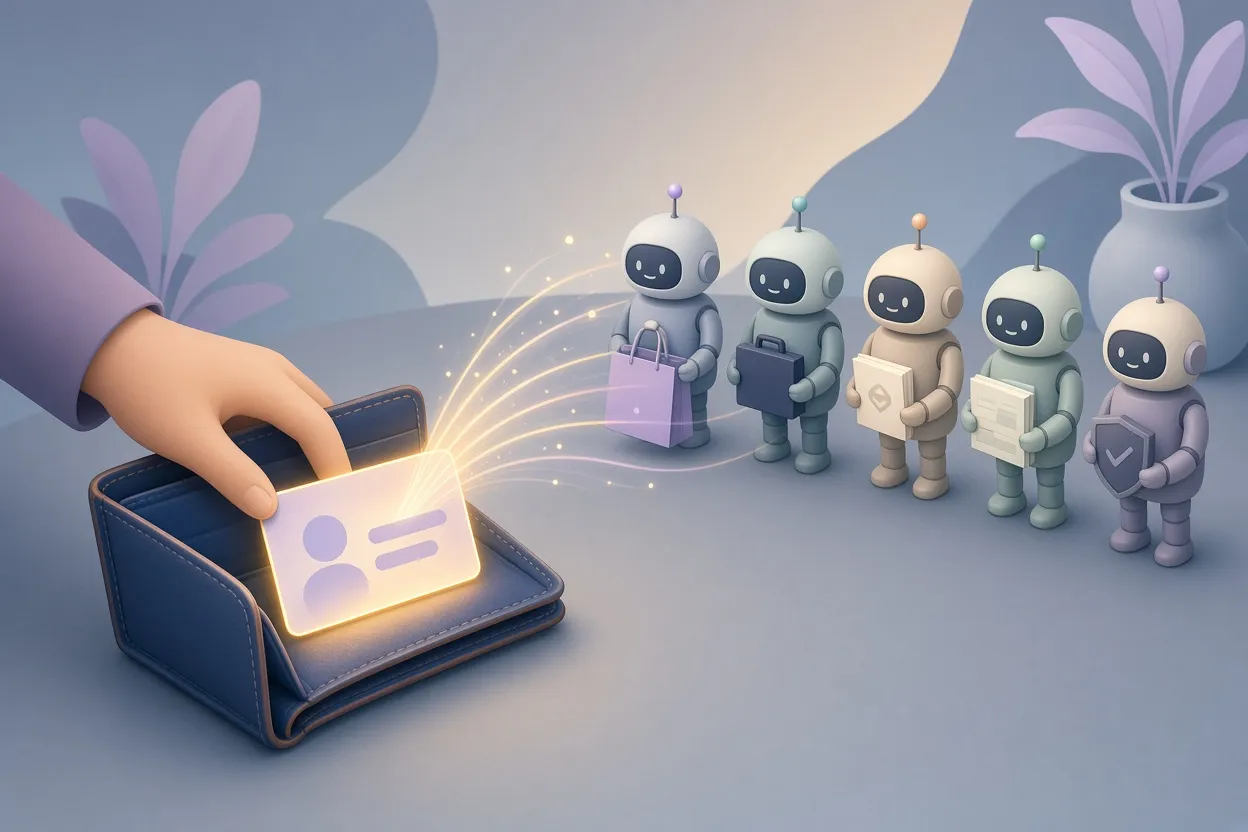
▲ One persistent credential shared across many agents
A recurring theme was that forcing users to re-prove their identity at every checkpoint creates recurring openings for deepfakes, altered documents and social engineering. Kinsel's alternative is a persistent cryptographic credential distributed across a unified network. Every user onboarded through Proof receives an IAL2-compliant, certificate-backed verifiable credential that is accepted across the company's network of 10,000 customer organizations. Once that credential exists, activities such as retirement withdrawals, e-commerce purchases and real estate sales run under network-maintained integrity, and the absence of fraud reports over time strengthens the credential's trust score.
He pointed to recent FinCEN guidance clarifying that verifiable credentials issued by private entities are acceptable under KYC (know your customer) and Customer Identification Program requirements. Government-issued digital IDs alone, he argued, will not solve commercial trust, because states do not accept liability for transaction fraud.
Looking toward late 2027, Kinsel predicted that consumers will manage several specialized agents, for example one for employment, one for personal finances and one tied to enterprise resource planning systems, with identity and financial credentials living in a portable personal wallet that travels across those agents, much as people carry a driver's license today. The credential would support selective disclosure, letting a user share only the data points a transaction needs.
Cost is part of the design. Kinsel criticized the practice of charging merchants high, repeated fees to verify the same customer again and again. Proof implements machine-to-machine payment for checks via HTTP 402 at 10 cents per check, with a stated goal of driving that lower.
From Notarize to transaction certainty
Proof's approach grows out of its history. The company launched eleven years ago as Notarize to solve remote online notarization, executed the first online mortgage closing in the United States, and expanded into wealth management, retirement accounts and automotive transactions. Along the way it worked to pass 47 state laws and several federal policies. Notarization requires proving who a person is, establishing what they did, and producing an independent verifiable record, which is the same structure now applied to documents, agreements and agents under the slogan "One verified credential. Every rail."
Kinsel drew a distinction from standard e-signature tools, which sign documents with corporate server certificates. Proof engineered PKI certificate infrastructure tied to individual human identities and embedded legal identity directly into document data. Visa invested in the company to bind payment rails to verified identity, and a partnership with Circle lets stablecoin transactions be cryptographically signed with a verified human identity.
He also cited the book "Electronic Value Exchange" as an inspiration. In the 1970s, retailers such as Sears discovered check fraud weeks later, recording bad checks in paper ledgers. In his view, title insurance, retirement services and wealth management still work that way. Payment platforms like Stripe succeeded by bundling payments, chargebacks, disputes and compliance into one package, whereas today's identity vendors sell disparate tools that leave fraud liability with the merchant. Proof's stated aim is a comprehensive authorization network with rules, pricing and network guarantees behind every trusted customer.
What merchants and fintech teams should do
Kinsel's sharpest warning was for merchants. Today, most lack awareness of, and control over, how agents check out on their stores, and those who simply refuse or ignore agents risk losing their customer relationships. His recommendations:
- Adopt UCP, the Universal Commerce Protocol championed by Shopify and Google, to expose product catalogs directly to buyer agents.
- Adopt verifiable intent protocols such as AP2 so that agents act with cryptographically proven consumer authorization.
- Define granular authorization parameters, such as exact item counts and price thresholds, instead of blanket permissions.
- Record cryptographically verified, legally admissible evidence of authorization to prevent chargebacks and rescission claims.
- Build on open frameworks such as FIDO, OpenID Connect, W3C Verifiable Credentials and PKI, and align operations with IAL2 and WebTrust-audited certificate authorities.
- Move fraud control from post-transaction dispute handling to real-time, pre-settlement authorization, which he called the priority for 2027 payments strategy.
He predicts the industry debate over blocking versus authorizing agents will be resolved by Money20/20 in late 2027, and he stated plainly that Proof intends to lead the market for agent identity.
Key points and next steps
The central claim is that agentic commerce cannot run on identity checks designed for account opening. Each action an agent takes needs a verifiable link back to a specific person and a specific permission, or businesses inherit legal and fraud exposure they cannot defend. x401 proposes that link using the familiar 401 status code, open standards and persistent credentials, with x402 handling the payment leg.
For fintech and commerce teams, the practical starting points are to audit where agents can already act on your platform without explicit consent, to decide how your catalog and checkout will be exposed to agents through protocols such as UCP and AP2, and to plan for authorization that happens before settlement rather than disputes that happen after. Whether Proof's protocol becomes the default is Kinsel's forecast, not a settled outcome, but the underlying design question, who approved this agent and for what, applies regardless of which standard wins.


